
Identity and runtime
Give each tenant an explicit identity and runtime boundary with owned lifecycle state.
Tenant isolation
Isolate tenants in an AI agent platform by separating runtime identity, workspace, credentials, storage, policy, sessions, logs, schedules, and access state for each tenant. Bewize Hub applies that model to managed AI worker runtimes with tenant-scoped control-plane records and operational evidence; it does not replace a buyer's own security evaluation.
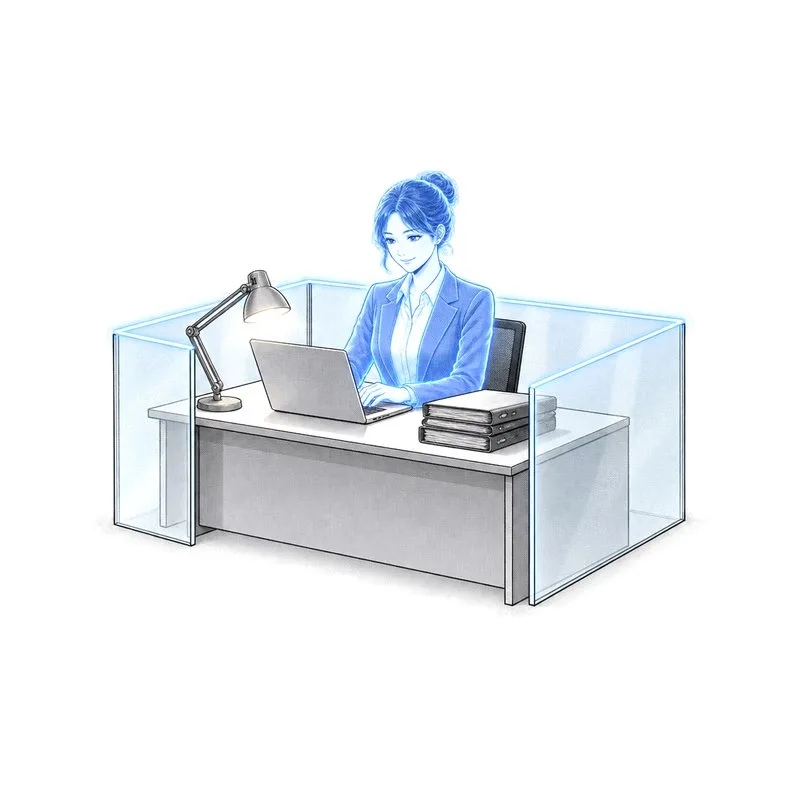
Tenant isolation is a set of boundaries, not a single checkbox.
Give each tenant an explicit identity and runtime boundary with owned lifecycle state.
Separate workspace, storage, environment keys, managed secret metadata, sessions, and logs.
Keep policy and access state tenant-aware, then inspect evidence after operational changes.
Review tenant isolation, managed secrets, policy APIs, access blocking, and redacted metrics.
Learn more →See tenant lifecycle, storage, schedules, A2A edge access, and run evidence.
Learn more →Plan host, release, storage, secret, and recovery ownership.
Learn more →Discuss runtime, data, credentials, policy, access, and evidence boundaries for managed agents.
Share a little context. Our team will reply by email to arrange the next step.